When Chrome email verification fails, first record whether the browser supplied a token, whether your server accepted it, and whether the form completed its intended action. Those are separate observations. Keep your existing email-verification route available, and investigate one failing case before changing the browser, verifier and issuer together.
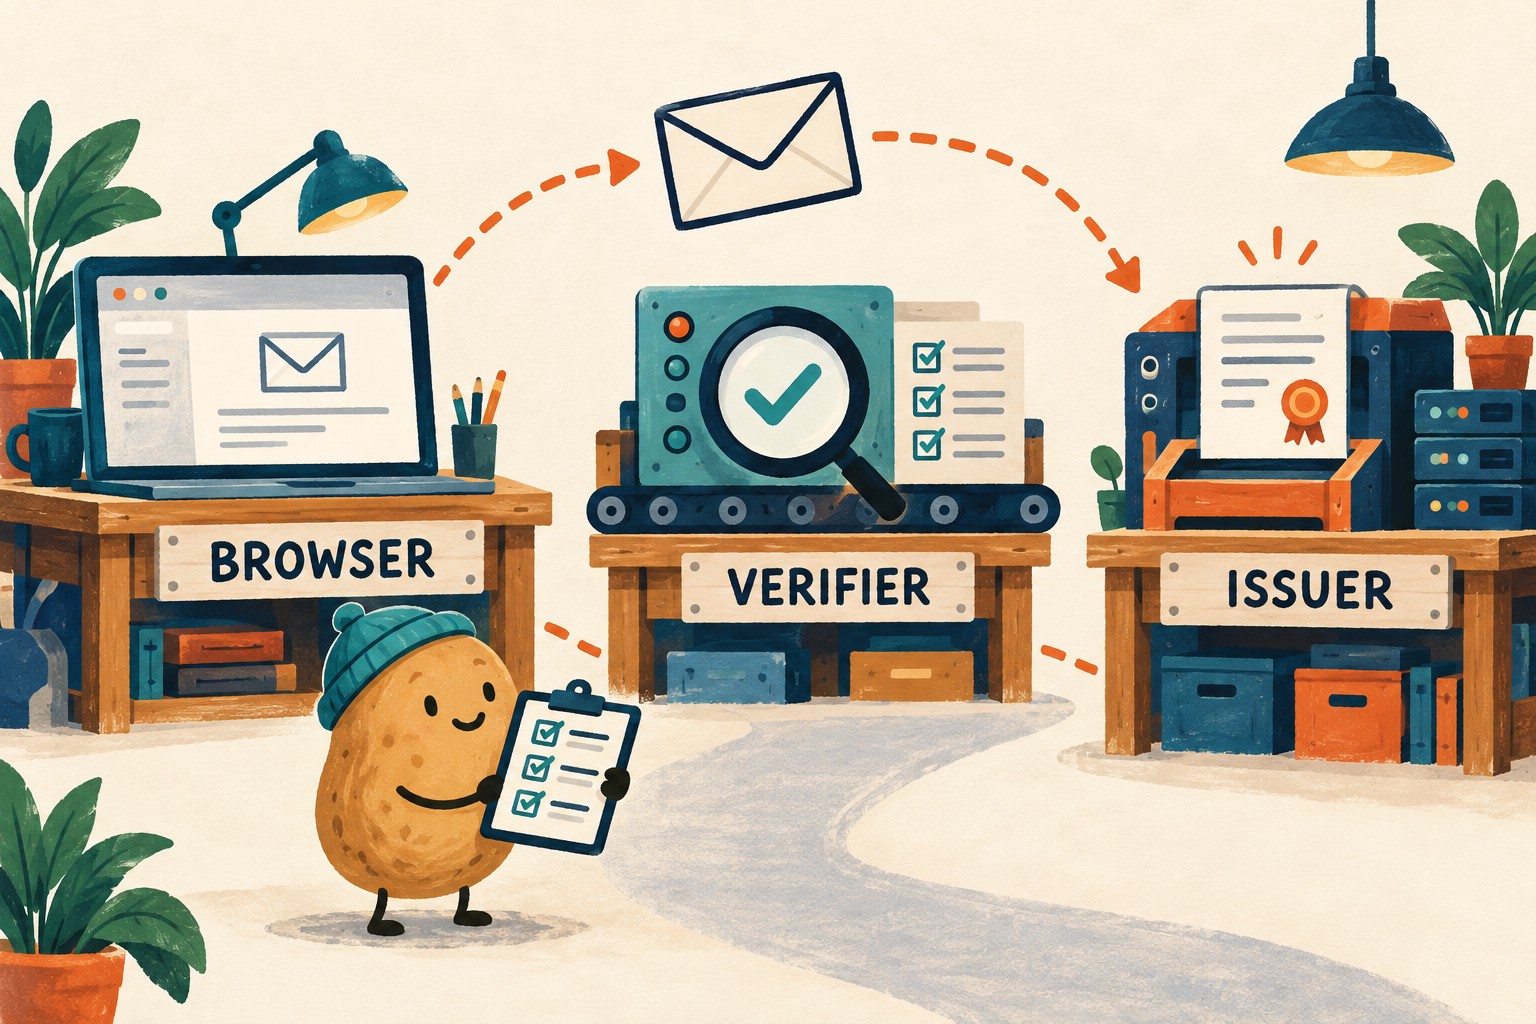
A spinner can make three different systems look like one broken button. This guide provides a proposed test plan for a team already evaluating Chrome's Email Verification origin trial. It is not a report of tests we ran, a complete security implementation, or evidence that every browser and provider supports the feature.
What changed, and which part do you own?
Google's October 5, 2026 update describes several version-specific changes: Android support and third-party origin trials from Chrome 154, with a same-site restriction on trial registration and issuer configuration; optional key identifiers during verification; and exact return of the submitted email value from Chrome 156. Issuers also need to account for a changed fetch-destination value from Chrome 154. These are origin-trial updates, not a statement of universal browser availability. See the official October update before choosing the versions for your test.
Start with ownership. If you operate a website that asks for an email address, you own the form and the verifier. An email provider owns issuance. A browser mediates the user experience. An SDK may cross more than one boundary, so write down who can actually change each component. Do not send an issuer-side task to the person who only owns the submit button.
Make a small, repeatable test environment
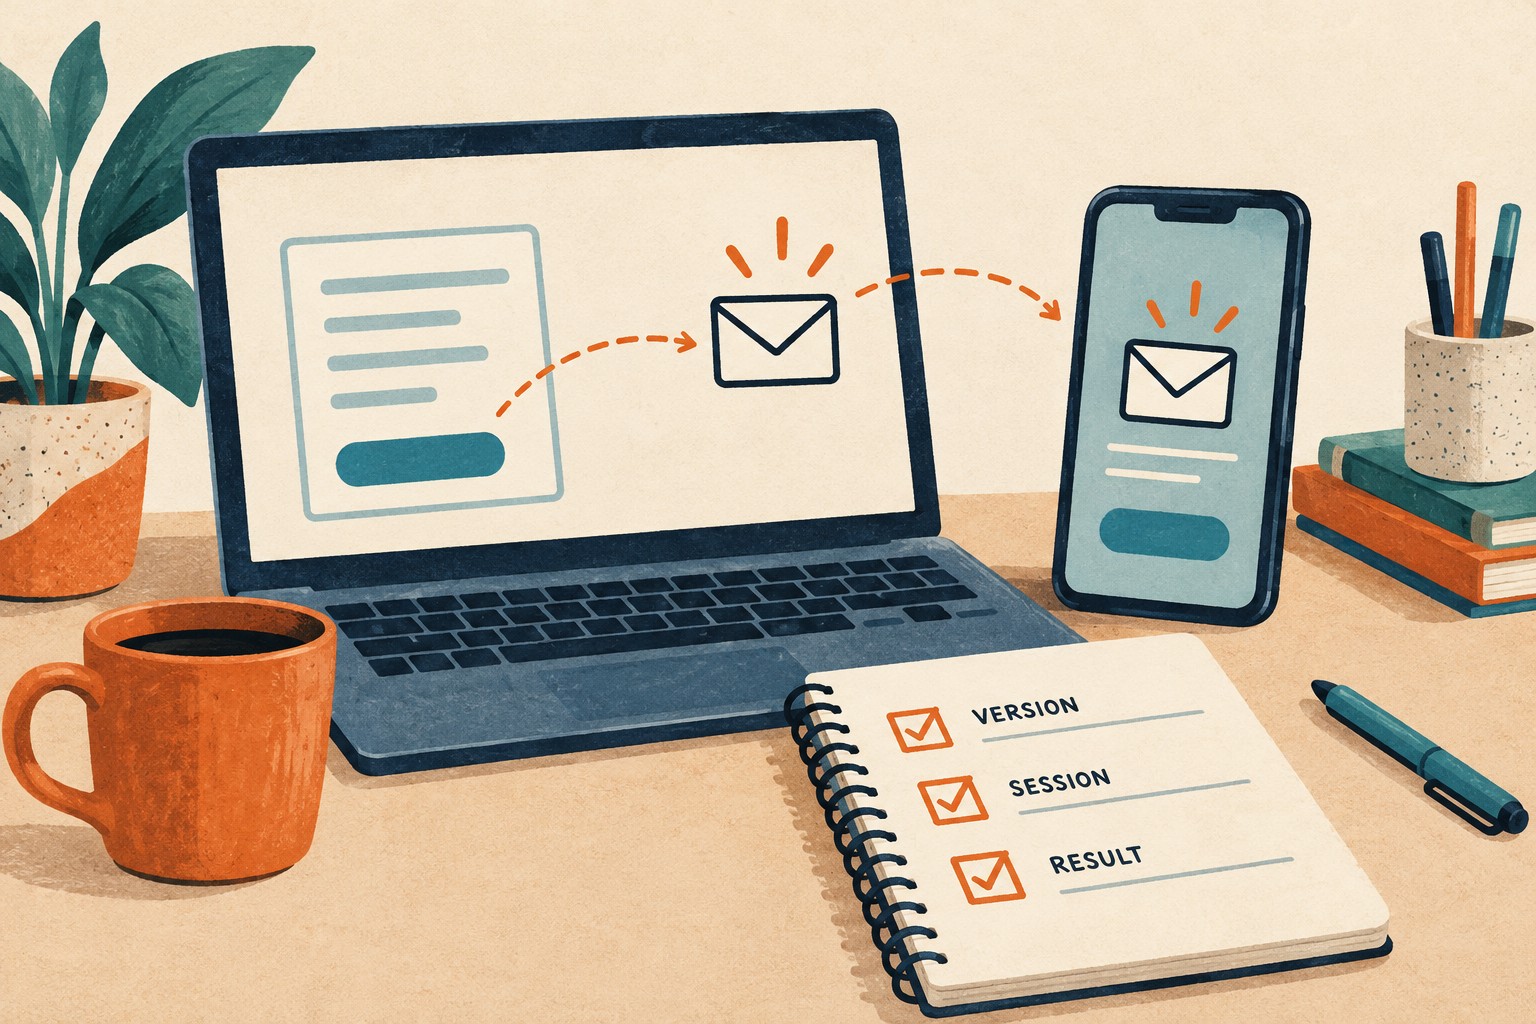
Choose a staging form and an approved test account. Write down the full browser version, operating system, verifier build, provider, trial configuration and participating email provider’s sign-in state in that browser profile. Give the case an ID that contains no personal email address. Keep this setup fixed for the first pass; “works on my phone” is not a reproducible environment.
Chrome's verifier guide says an empty token can mean unsupported browser/provider behavior or skipped verification, and directs the site to its existing OTP or verification-link route. A present token still needs server-side validation: expected claims and session values, issuer delegation, signatures and key binding. A filled field or a visible checkmark is not your application's acceptance decision. Use the complete relying-party implementation guide; this checklist does not replace those checks.
- Run your existing route first. Confirm that the approved test user can complete it. Record the landing state after completion, not merely that an email was sent.
- Try the trial-enabled route. Note the browser's visible state, whether the server received a token, the validation result category and the resulting form state.
- Exercise the empty-token route deliberately. Use a supported test setup that produces no token. Check that the alternative is discoverable and that the user can finish.
- Repeat one changed condition. For example, compare sessions signed in to and signed out of the participating email provider using the same browser build. Do not also change the SDK and server in that comparison.
Record categories and case IDs in the shared worksheet. Keep full tokens, cookies, session values and personal addresses out of screenshots, tickets and public bug reports. Follow your team's approved diagnostic-data handling when deeper investigation is necessary.
Turn the update into test cases, not a blanket upgrade verdict
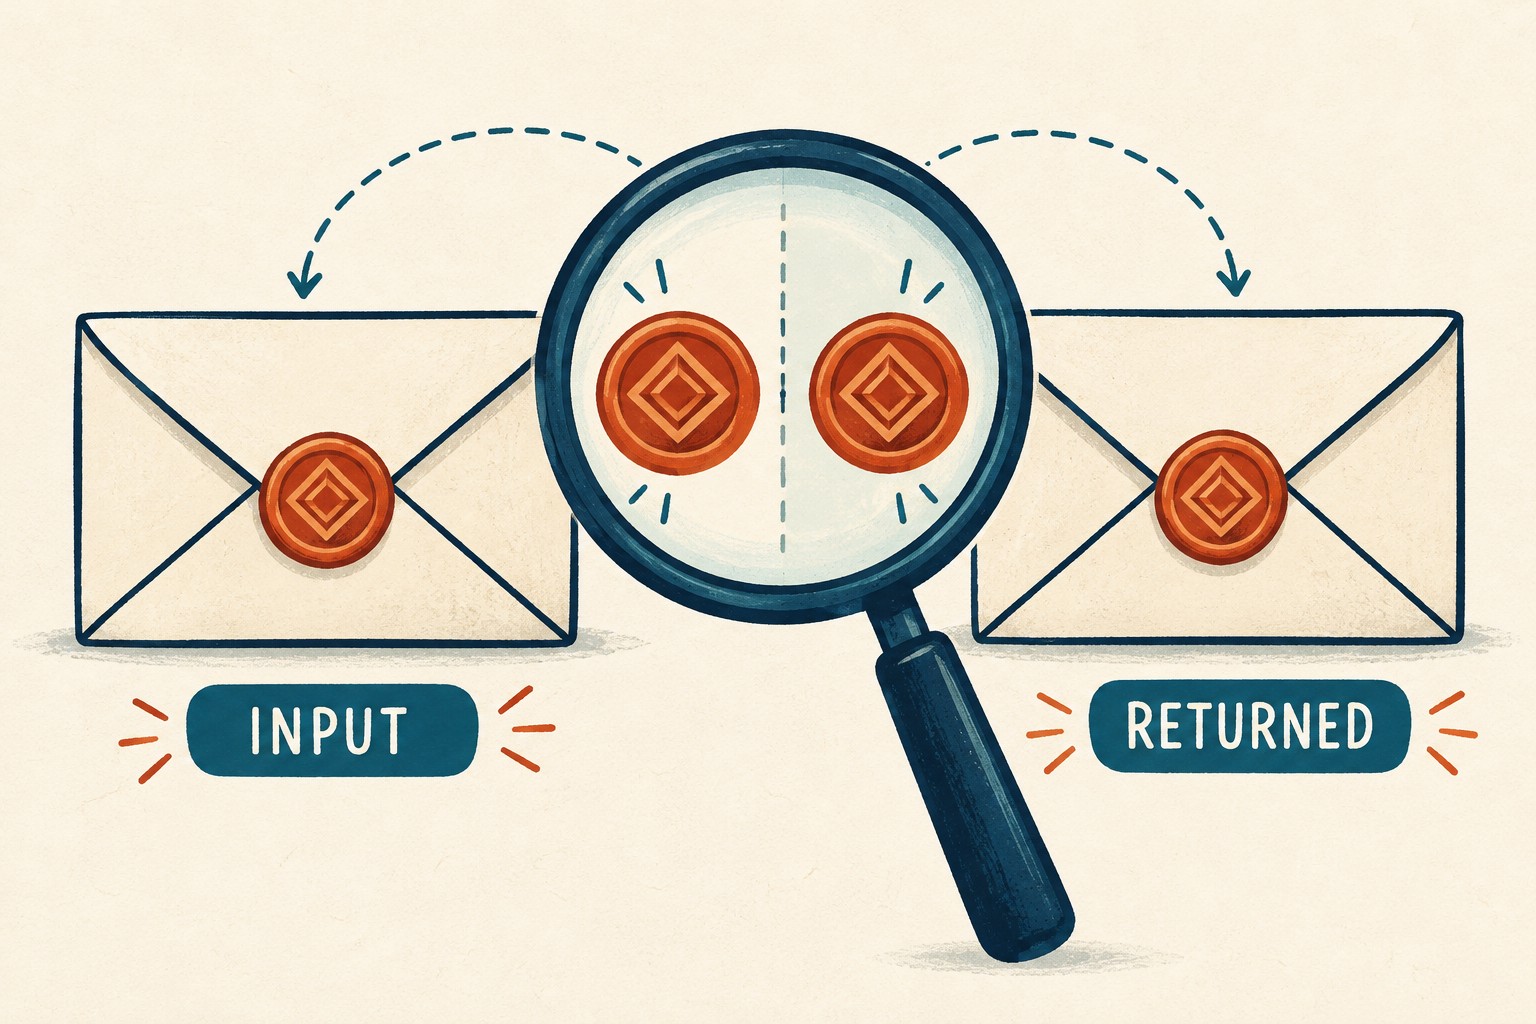
Use the following as a starter matrix. “Expected” means the result your implementation should demonstrate in its controlled test environment, not a result already observed here. Add the browser version and an owner to each row.
| Case | What to observe | Useful completion evidence |
|---|---|---|
| Normal trial flow | Browser response, server decision and completed form action | All three observations attached to one case ID |
| No token supplied | Whether the existing verification route appears and finishes | A completed alternative route, not only its first screen |
| Token rejected in a controlled negative test | Whether the form avoids marking the address verified | A rejection category and a clear recovery route |
| Provider returns no key identifier | Whether the verifier follows the documented key-discovery path | A server-side test result reviewed by the verifier owner |
| Submitted email formatting | Input value and returned value under the version being tested | A synthetic or approved test-case comparison, with the applicable version rule |
| Issuer request compatibility | Whether the issuer handles the documented fetch-destination change | An issuer-owned compatibility result for the supported version range |
The last three rows target changes named in the October announcement. If your team does not operate an issuer, mark its row “external dependency” and identify the contact or documentation you rely on. Do not mark it passed because the website's own checks are green.
Triage the first divergence
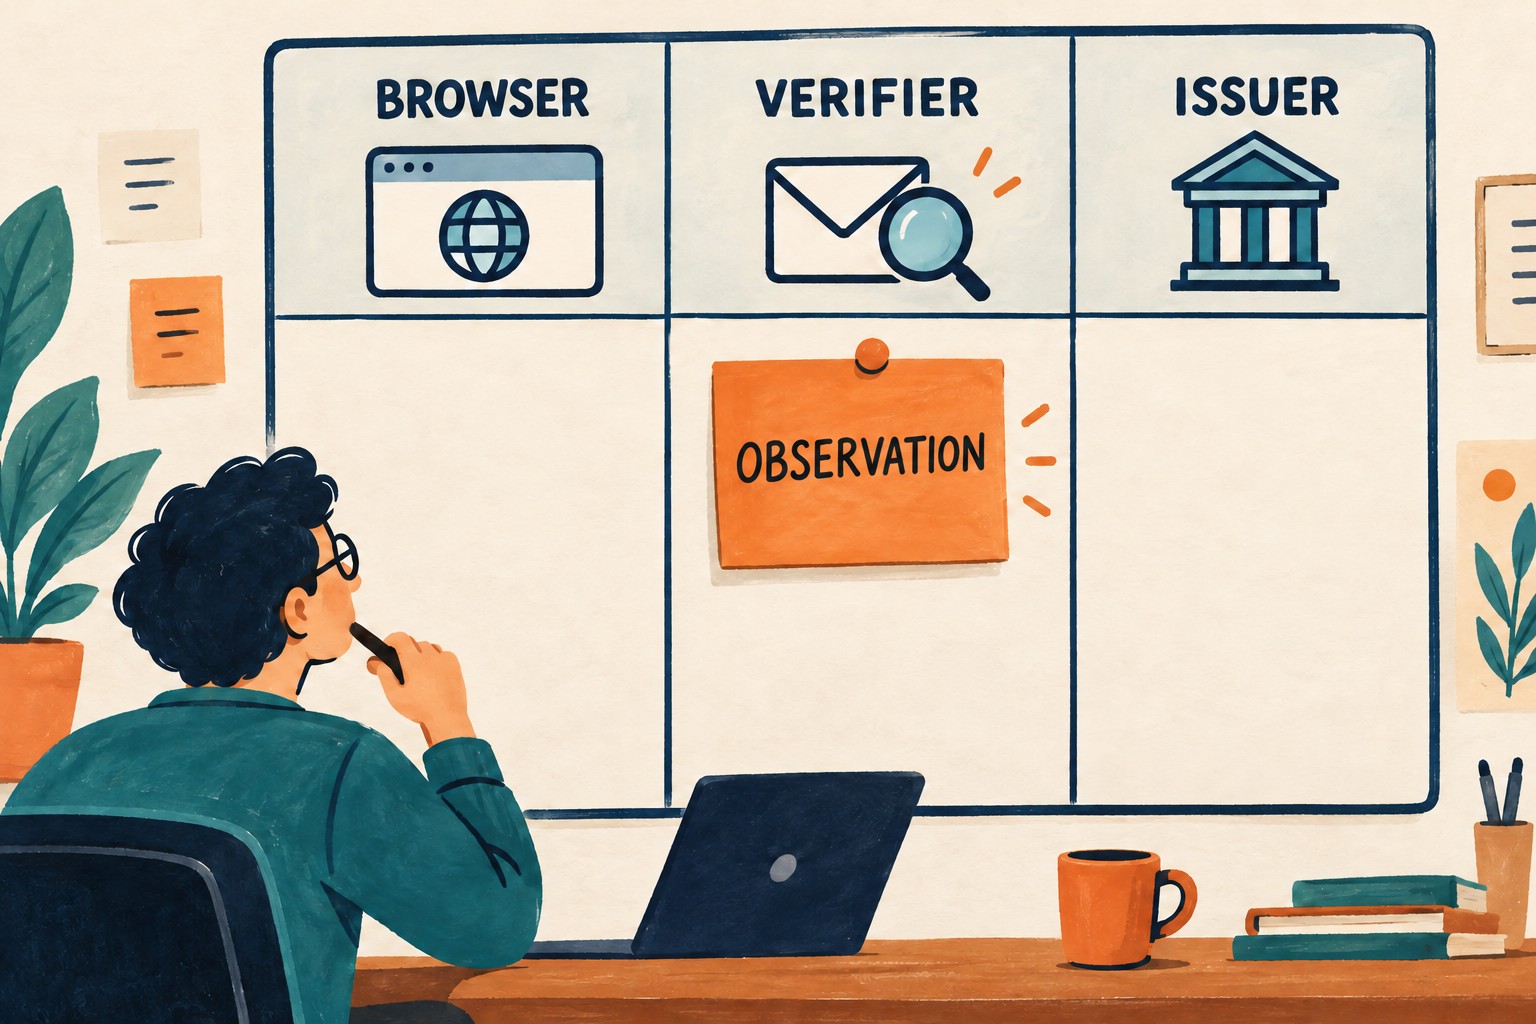
Suppose a hypothetical case reaches the browser's completion state, but the form returns the user to the same screen. The useful report is not “Chrome is broken.” It is: “Case E-03 reached the browser completion state; server validation outcome is unknown; form stayed on step one.” The next action is to establish the missing server observation.
If the server rejected the token, hand the case to the verifier owner with a safe error category. If the server accepted it but the form did not progress, inspect the application's post-verification transition. If no token arrived, first record the actual environment and alternative-route behavior. Each route narrows the next investigation without claiming a root cause before evidence exists.
Do not make a negative test pass by removing validation or accepting an unverified address. A useful test exposes a boundary; it does not erase it.
Copy this handoff record
- Case and task: [ID] / [what the user was trying to finish]
- Environment: [browser full version] / [OS] / [verifier build] / [provider] / [trial setup]
- Changed condition: [one variable, or none for the baseline]
- Expected: [visible result and server decision, with the applicable documentation link]
- Observed: [browser state] / [token present or absent] / [safe validation category] / [form outcome]
- Alternative route: [available? completed? where did it stop?]
- Owner and next action: [person or team] / [one bounded investigation] / [retest condition]
Finish the review when each required case has an observed result, failures have an owner, and the existing verification route still completes. Keep “not tested” visible. A smaller truthful record is more useful than a large sheet of optimistic checkmarks.
For the broader task of preserving a reproducible environment and next action between sessions, use our AI coding handoff guide. It complements this verification-specific record without turning it into a security certification.