Before replacing a key or retrying a failed AI request, record four things: the endpoint, HTTP status, structured error code and credential mode. A status number by itself is not a diagnosis.
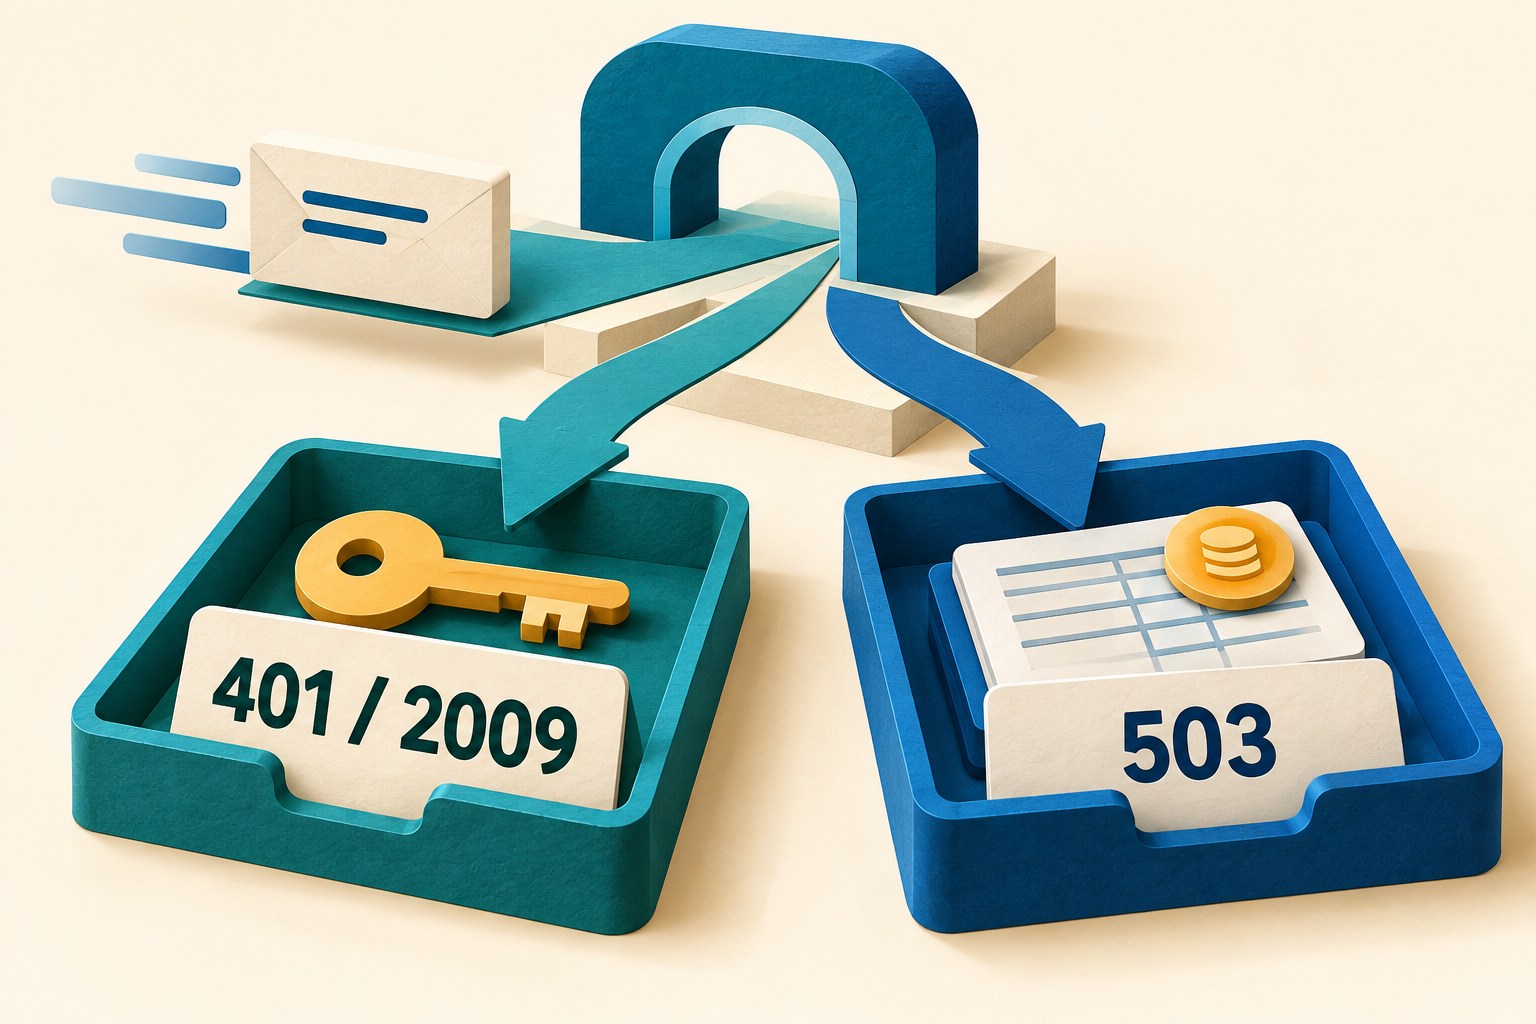
Cloudflare's October 6, 2026 announcement standardizes provider-rejected credentials on POST /ai/run as HTTP 401 with code 2009. Under Unified Billing, the announced provider-rejection response is 503 instead. The Google Vertex case also stops upstream retries. The notice does not establish the same change for every gateway endpoint.
Source: Cloudflare's provider-credential error announcement
Start with the request you actually made
Use the worksheet below for one observed request path. If a service uses more than one endpoint family, make separate cards. Do not let a common SDK name stand in for the URL the client actually called.
Record the hostname, HTTP method and path pattern, with account identifiers sanitized for the audience. Keep the time, environment and application build beside that record. If an intermediary changed the response, note where your observation was captured. Leave missing evidence marked unknown rather than reconstructing it from memory.
Separate Cloudflare access from provider credentials
The REST API authentication reference gives another reason for a 401: on /accounts/{account_id}/ai/*, a Cloudflare token with only AI Gateway permissions returns code 10000. The documented requirement is Account > Workers AI > Read. That example concerns access to Cloudflare's API, not proof that a provider key was rejected.
The authentication guide also distinguishes headers: REST requests at api.cloudflare.com use Authorization for the Cloudflare token; provider-native requests at gateway.ai.cloudflare.com use cf-aig-authorization. Check the documentation for your endpoint family before copying a header example from another route.
Use these distinctions to assign an investigation, not to justify broadening permissions. An authorized administrator should review any credential or access change through the existing process. Keep token values out of tickets, screenshots, fixtures and chat messages.
Confirm the credential mode before choosing an owner
Cloudflare's credential-precedence documentation describes applicable provider credentials on the request, then a stored provider key under the default alias, then Cloudflare-managed Unified Billing credentials. The Cloudflare access token is a separate credential; do not classify it as a supplied provider key merely because its header says Authorization.
The BYOK alias documentation distinguishes direct provider-passthrough alias selection from Unified Billing routes, which consult the default key. A key stored under another alias is not sufficient evidence that a particular request used it.
Ask the responsible owner to confirm the selected mode from authorized configuration and sanitized request evidence. The worksheet should say what supports the conclusion. “We usually use our own key” is a lead to check, not a completed finding. If the mode remains unknown, retain that uncertainty in the handoff.
Make retry behavior a separate review
The gateway's request-handling documentation exposes retry controls including attempts, delay and backoff. That does not tell you what your client or scheduler does. Inventory each layer separately before changing any production behavior.
- Application or SDK: which outcomes cause a repeat, and where is the limit recorded?
- Gateway: which applicable configuration or request overrides were in effect?
- Job runner: can it restart the whole operation after the client finishes?
- Manual action: could someone launch another attempt while the existing work is unresolved?
For this review, require a named owner and a documented stopping condition. Do not infer that every server error is temporary, or that every authentication-related error should be handled identically. An unknown response needs investigation; it should not silently inherit whichever retry branch is most convenient.
Consider a fictional service whose SDK repeats server errors and whose scheduler also restarts failed jobs. An operator sees failures and proposes replacing a stored provider key. Before approving that change, the card asks whether this request actually used that key and whether the two repeat mechanisms are both active. This example illustrates questions to resolve, not an observed Cloudflare incident or a measured retry count.
Rehearse the classification without live requests
Prepare synthetic responses in an isolated local test harness using your application's existing testing tools. Test the investigation label, the user-facing message and the stopping behavior. Do not send dummy credentials to a live provider, purchase credits or change production authentication merely to create a failure.
| Synthetic case | What the rehearsal should establish |
|---|---|
| The announced provider-rejection case | The application preserves the status and structured detail and selects the intended investigation branch. |
| The documented Cloudflare permission example | The message directs the authorized owner to the access boundary rather than assuming the provider key failed. |
| The managed-credential exception | The handler retains the confirmed credential mode and follows the explicitly reviewed server-error policy. |
| Missing structured code or unreadable body | The result remains unclassified, with enough sanitized context for follow-up. |
| Unknown endpoint or credential mode | The handler does not claim a diagnosis that its evidence cannot support. |
Keep fixture inputs and expected labels explicit, including the case where evidence is absent. A passing mock test proves only that the tested application logic handled those inputs as expected. It does not establish that real credentials work, that a provider is available or that production has the same configuration.
Copy the credential-triage worksheet
This is a practical review aid, not a Cloudflare API schema. Fill it from existing authorized evidence and link to the protected internal record when appropriate.
| Field | Record |
|---|---|
| Observation | Time and timezone, environment, build, and where the response was observed. |
| Request route | Hostname, method, sanitized path pattern, provider and model. |
| Response evidence | HTTP status, structured code if present, and a sanitized request or log reference. |
| Credential mode | Applicable supplied provider key, default BYOK, managed billing or unknown; include supporting evidence without secret values. |
| Repeats | Client, gateway, job-runner and manual behavior; owner and stopping condition for each relevant layer. |
| Rehearsal | Fixture identity, expected classification, observed result and untested cases. |
| Handoff | Next owner, approved next action, unresolved facts and next check time. |
Close the review by distinguishing a supported diagnosis, an unresolved question and an action somebody actually completed. If a change is later approved, record its result separately. This guide is based on documentation checked October 7, 2026; it does not claim a live API trial. Its useful outcome is a precise next investigation, with fewer assumptions hidden behind one status number.